Breaking
Latest health news from South Africa and around the world•Wellness, nutrition, and fitness updates daily•Medical breakthroughs and healthcare updates•Science-backed health explainers and guides•Health tech, reviews, and upcoming events•
 SA Health News Desk
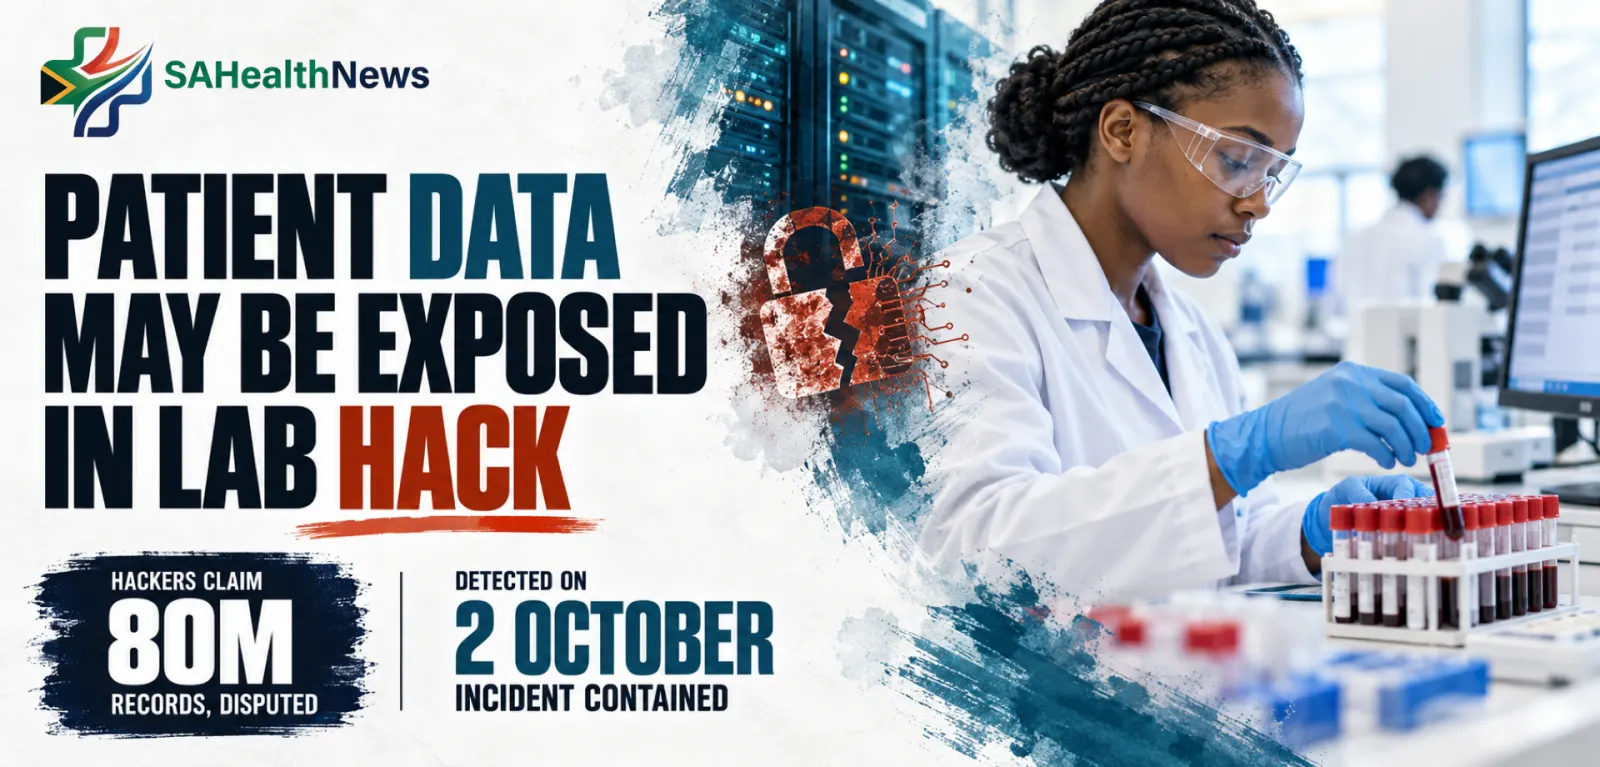
Ampath says patients' ID numbers, contact and medical aid details may have been accessed in a cyberattack, but disputes the 80 million record claim.
Ampath, one of South Africa's largest pathology laboratory groups, has confirmed that attackers got into part of its IT systems and that patients' personal details may have been taken. The company has notified the Information Regulator but disputes a hacker group's claim that more than 80 million patient records were stolen.
Ampath says it detected the incident on 2 October and that it has been contained. It became public on 13 October, when a group calling itself ByteToBreach claimed responsibility on a hacker forum and posted screenshots, MyBroadband reported. Ampath's website went offline that day and was partly restored by the evening.
ByteToBreach says it fully copied 10 of Ampath's 375 databases, covering patient, employee, finance and provider data from the mid-2000s to the present. It says one admission table alone holds more than 80 million records, and that ransom "negotiations were short". It did not say whether money was demanded or paid.
Ampath says the 80 million figure "should not be interpreted as 80-million individual patients". It appears to count database entries, and one patient can generate many entries over years of tests. The company says the number circulating overstates how many people may be affected, and has asked the public to treat the attackers' claims with caution until they are independently verified.
According to Ampath, the information that may have been accessed is mainly demographic and administrative. Depending on the record, it can include names, ID numbers, dates of birth, age, sex, home language, addresses, email addresses and mobile numbers. Medical aid details (scheme name, membership number and option) and payment records (payer name, payment reference, amount, and transaction date and time) may also be involved. Not every record contains every field.
The company says that so far there is no evidence that medical records, diagnoses, pathology test results or banking information were compromised. Its findings are still subject to forensic verification, and the investigation, with independent forensic specialists and legal advisers, is continuing.
Ampath says it has blocked malicious IP addresses, restricted access to affected systems, disabled exposed accounts and credentials, removed unauthorised files and restored systems from clean backups. It reports no sign of ongoing unauthorised access and no disruption to laboratory or patient services.
Ampath says it reported the breach to the Information Regulator under section 22 of the Protection of Personal Information Act (Popia). That section requires an organisation to notify the regulator, and the people affected, when there are reasonable grounds to believe their personal information has been accessed by an unauthorised person. The regulator has not commented publicly.
Ampath has warned that the exposed details could be used for fraud, impersonation, phishing and email scams. It has urged patients to be alert to suspicious messages, particularly any request for banking or financial information.
The company says it will give further updates as verified information becomes available.
Sources: Ampath statements reported by MyBroadband (13 and 14 October 2026), ITWeb and IT-Online (15 October 2026), Bizcommunity (14 October 2026) and MedicalBrief (14 October 2026).
Source: SA Health News